01 · The idea
In everyday language
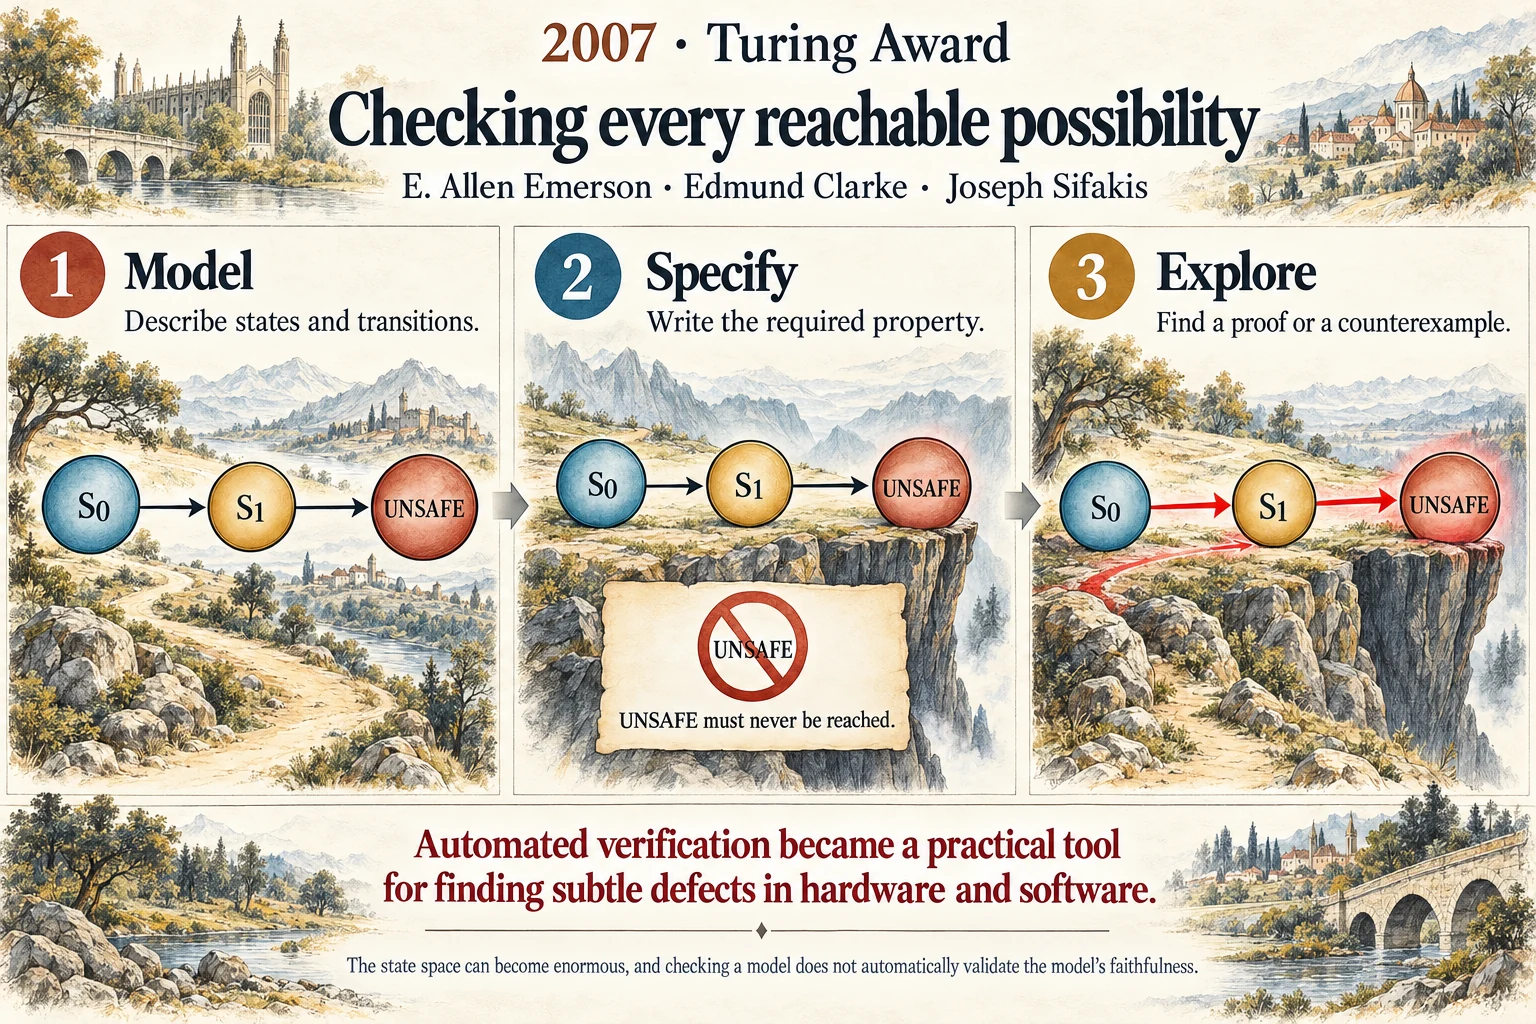
Edmund Clarke, E. Allen Emerson and Joseph Sifakis developed model checking. A finite model describes a system’s states and transitions; a logical property describes what should hold. An algorithm explores the model and can return a counterexample showing how a requirement fails.
Why it matters
Automated verification became a practical tool for finding subtle defects in hardware and software.